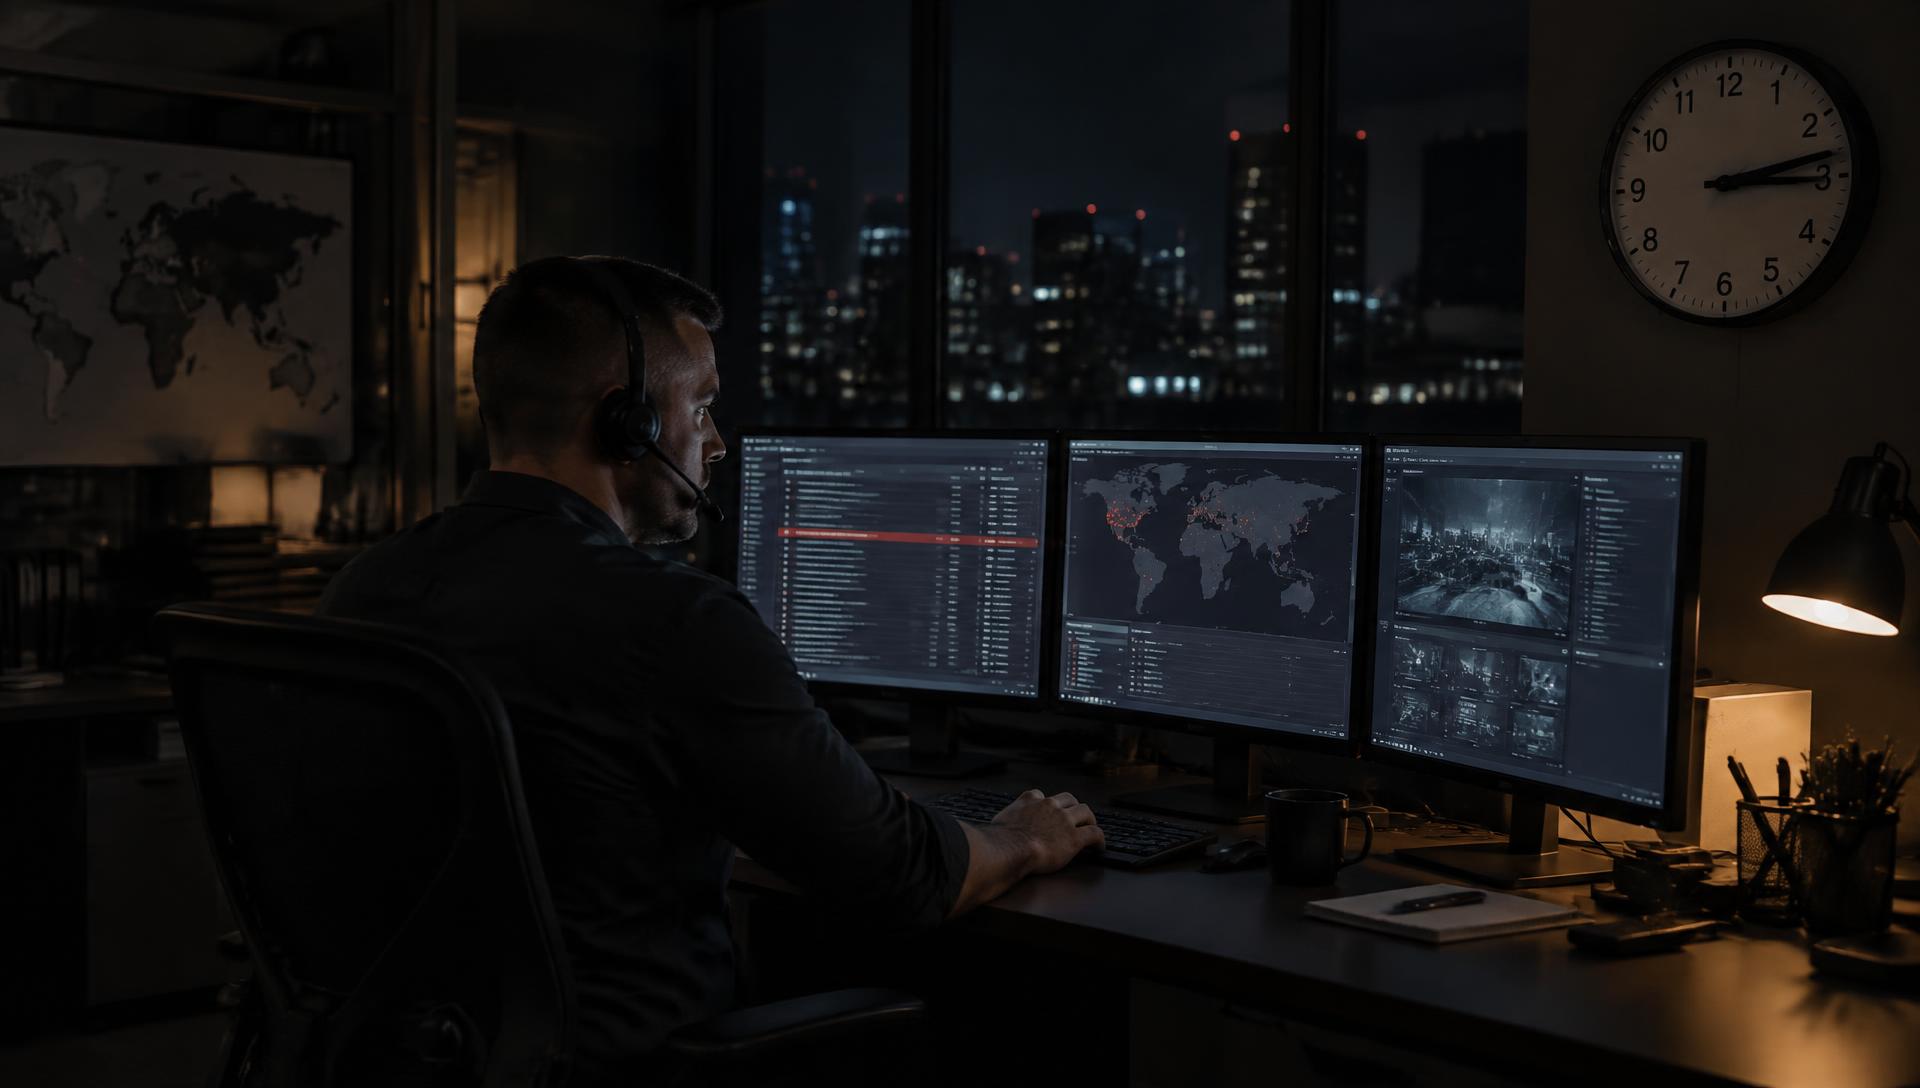
Analyst on shift in the BlackBunker operations center at 2:14 a.m.
24/7 SOC and MDR. Staffed by US military veterans. On US soil.

They only need to get in once. We watch every second.

BlackBunker is a 24/7 security operations center for SMBs in healthcare, finance, legal, and defense. Every alert is triaged by a US military veteran analyst with the authority to contain the threat, not just report it. Twelve-minute response commitment, in the contract. From $3,500 a month.

12-min analyst response100% US veteransUS citizens, US soilLive in one week
100% US Veterans·Led by a Retired Army Cyber Officer, CISSPCleared-Experience Analysts·100% US-Based, US Citizens
$20.9B

lost to cybercrime in 2025, up 26% in one year

$3.05B

lost to business email compromise alone

$893M

lost to AI-enabled fraud, the first year the FBI tracked it

Source: FBI IC3 2025 Internet Crime Report

// The watch, in numbers.

The numbers behind the watch.

12 min

analyst response SLA, written into the contract

24/7/365

live eyes on screen, never an empty chair

Who we watch for.

[NEED: client logo or anonymized descriptor]
[NEED: client logo or anonymized descriptor]
[NEED: client logo or anonymized descriptor]
[NEED: client logo or anonymized descriptor]
[NEED: client logo or anonymized descriptor]
[NEED: testimonial, name or role and industry]
[NEED: testimonial, name or role and industry]
AI detection, human decision100% US veteran analystsCleared-experience up to Top SecretUS soil, never offshoreDeploys in under an hour12-min analyst SLA
// The new attack surface

The attack that gets you will not look like malware. It will look like AI.

Your CFO's voice, cloned.

A 40-second sample from a webinar is enough. The wire goes out before anyone questions it.

Your executives, for sale.

Home addresses, phone numbers, and family details sit in data broker databases waiting to be weaponized.

Your credentials, already leaked.

The breach that exposes you probably already happened, at a vendor you forgot you used.

Point tools do not catch any of this. AI detection plus a human on shift does.

// Watched by warfighters

The people on shift stood watch for the country before they stood watch for you.

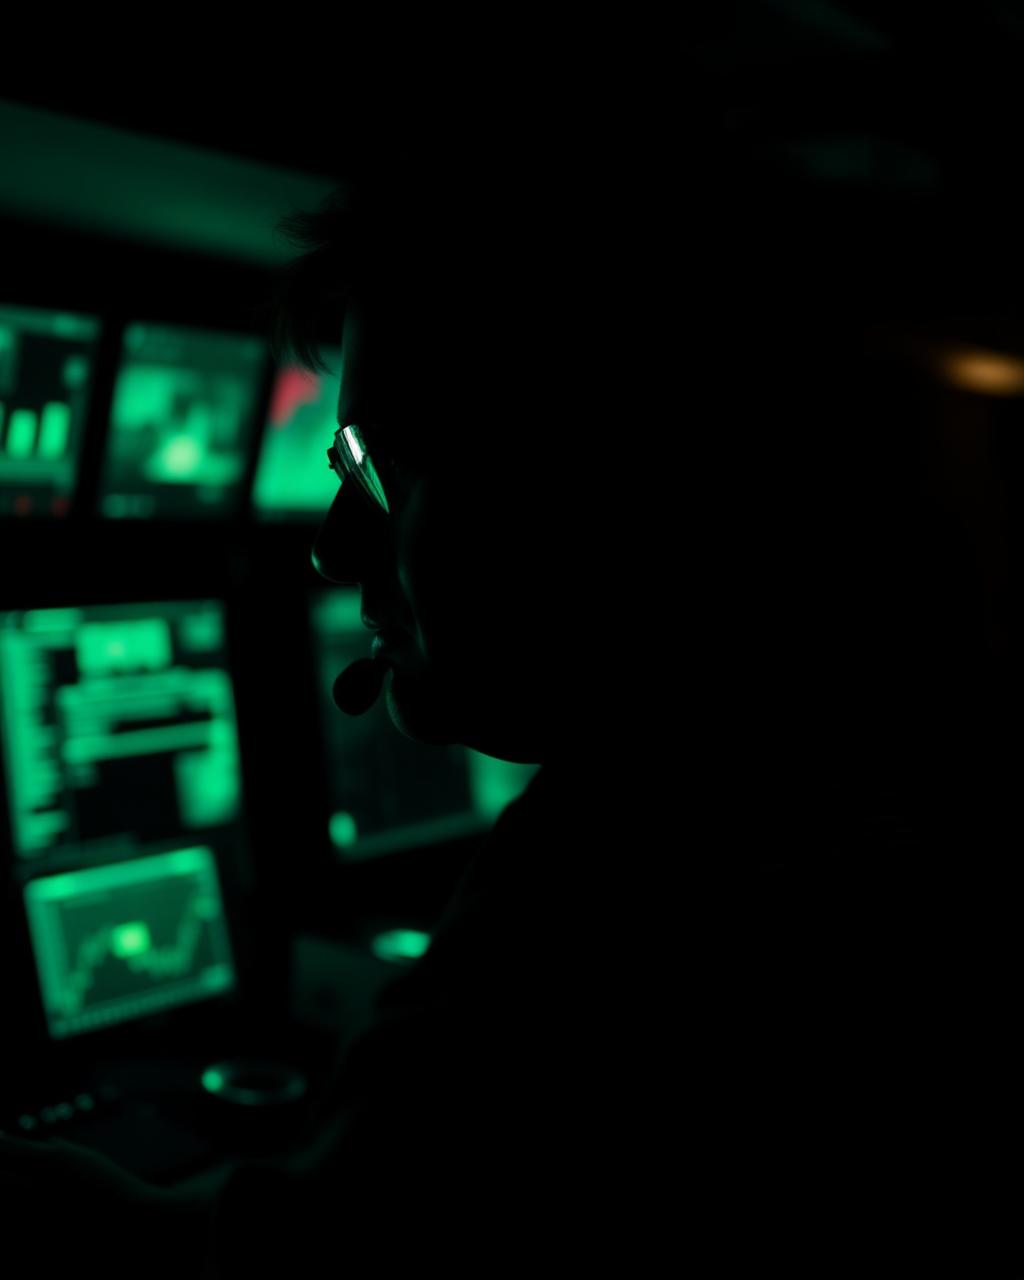
US veteran cyber analyst watching threat monitors in the BlackBunker security operations center
Analyst on shift

Speed to contain

Veterans trained in operations centers act on incomplete information under time pressure. That is where the 12-minute SLA comes from, and why most containment happens faster.

Discipline you can audit later

Shift handoffs, incident logs, chain of custody. You get an incident timeline you can hand to counsel or an insurer.

Trust that survives scrutiny

100% US citizens, working on US soil, many with cleared experience up to TS/SCI. No offshore queue, no subcontracted night shift.

Many of our analysts came from special operations. The watch is run by a retired US Army cyber officer, CISSP, with 23 years of service.

[NEED: analyst headcount and credential counts]
How we staff the watch
// Seven hours of silence

The breach happens at 2 a.m. You find out at 9.

  1. 2:14 a.m.

    An attacker logs in as your controller using credentials stolen from a vendor you forgot. Your EDR fires an alert. It lands in an inbox.

  2. 4:00 a.m.

    They have mapped your file shares.

  3. 6:00 a.m.

    Encryption starts.

  4. 9:00 a.m.

    Your office manager calls. Nothing opens.

  5. 9:30 a.m.

    You are paying an incident response firm $400 an hour to reconstruct what a person on shift would have stopped in a minute. Then breach counsel. Then notification letters. Then your insurer asks why nobody was watching.

Seven hours of silence is the entire attack. We remove the silence.

  • Your alerts go to an inbox nobody reads until Monday.
  • You have eleven security tools and zero people watching them.
  • Your MSP resets passwords. Nobody hunts threats.
  • You'd find out about a breach the same way your customers would: after the damage.

Four things a dashboard cannot do.

Live human triage, 24/7

A veteran analyst reviews every alert that matters within 12 minutes, day or night. You stop paying attention to alerts because someone else already is.

Active containment and incident response

We isolate the host, kill the session, revoke the token, and block the infrastructure before we call you. Incident response is on retainer, not on a purchase order.

Deepfake and executive impersonation defense

We detect cloned-voice and lookalike-email attempts against your executives and finance team, and we drill your people on the wire-approval moment.

Dark web and data broker monitoring

We find your leaked credentials and your executives' home addresses before an attacker uses them.[NEED: confirm broker removal is in scope]

Every BlackBunker engagement runs on our downloadable platform, deployed across your devices, networks, and accounts. It detects, prevents, and responds to cyber threats, impersonation, and deepfake attacks. It watches the dark web for your exposed data. And it feeds everything to our 24/7 security operations center, where a US-citizen veteran analyst is on shift 24/7/365. During onboarding we walk you through exactly which components are deployed in your environment and what each one sees.

Built for regulated industries: healthcare, fintech, legal, defense, manufacturing.

// How it works

From signed contract to live protection in one week.

  1. 1Day 1

    Deploy

    Lightweight agent on endpoints, read-only API connections to Microsoft 365 or Google, identity, and cloud. Under an hour in most environments. No rip and replace.

  2. 2Days 2 to 5

    Tune

    Your named analyst pod baselines what normal looks like for your users and devices, so alerts mean something.

  3. 3Day 6 onward

    Watch

    Live eyes 24/7/365. Containment authority agreed in writing. Monthly report your leadership can read.

// A tool alerts you. A SOC defends you.

The rest send you notifications.
We send someone into the fight.

CapabilityHelp-desk MSPPoint tools (Defender, AV)Alert-only MDRBlackBunker
Live human eyes on screen 24/7
Active containment and incident response
Deepfake and impersonation defense
100% US-citizen, US-veteran team

Full comparison: MDR vs MSSP

What a shift looks like.

02:14 EST. A credential-stuffing attempt against a finance workstation. Our SLA is twelve minutes. This one had an analyst on it in under sixty seconds, session killed and endpoint quarantined before anyone woke up. The client read about it in the morning report.

Representative scenario. Client engagements are confidential.

// What it costs

A full 24/7 security operations center,
for less than one in-house hire.

One in-house lead runs $180K to $250K+ all-in[NEED: source for in-house cost range] and still sleeps eight hours a night. BlackBunker never blinks, for about 75% less. SOC as a service starts at $3,500 per month.

WATCH

For companies with 25 to 150 people that own security tools nobody watches.

Core SOC coverage. Human eyes on every alert, around the clock, from the first week.

For teams that need a real 24/7 watch on their environment right now.

  • Platform deployment
  • 24/7 monitoring
  • Analyst-triaged alerts
  • Dark web monitoring
  • Monthly threat report
Starting at $3,500/mo
Book a Call
Most popular

COMPLETE DEFENSE

For companies that wire money, hold client data, or answer to a board.

Full MDR. One contract that replaces 8 to 12 vendors and the people to run them.

Everything in Watch, plus active response and executive-grade defenses.

  • Active containment and response
  • Incident response on retainer
  • Deepfake and impersonation defense
  • Identity and privacy protection
  • Board-ready reporting
From $9,500/mo
Book a Call

REGULATED

For defense contractors and high-assurance environments handling CUI.

Built for ITAR, CMMC, and CUI environments. Defense, healthcare, and high-assurance work.

Complete Defense in a restricted enclave, run by a US-citizen pod.

  • Contractual US-citizen-only staffing
  • GCC High or Azure Gov enclave
  • CUI handling, chain of custody
  • Screening to NIST 800-171 3.9.1
  • Analysts with prior TS/SCI experience
Custom
Book a Call

Month-to-month after onboarding. No long lock-in.

Savings calculator
50
$4,000
In-house est.
$280,500/yr
BlackBunker est.
Recommended: Watch
$42,000/yr

Estimated savings: $238,500/yr

A 50-employee company spending $4,000 per month on security tools would spend roughly $280,500 per year building this in-house. The Watch tier covers that same company at $42,000 per year, an estimated saving of about $238,500 per year.

Representative target outcomes, not client-attributed results.

Included in every tier.
  • Onboarding and tuning handled by our team, with coverage live in the first week.
  • A named analyst pod that learns your environment instead of a rotating queue.
  • Monthly reporting your leadership and your insurer can both read.
// Leadership

Who runs BlackBunker.

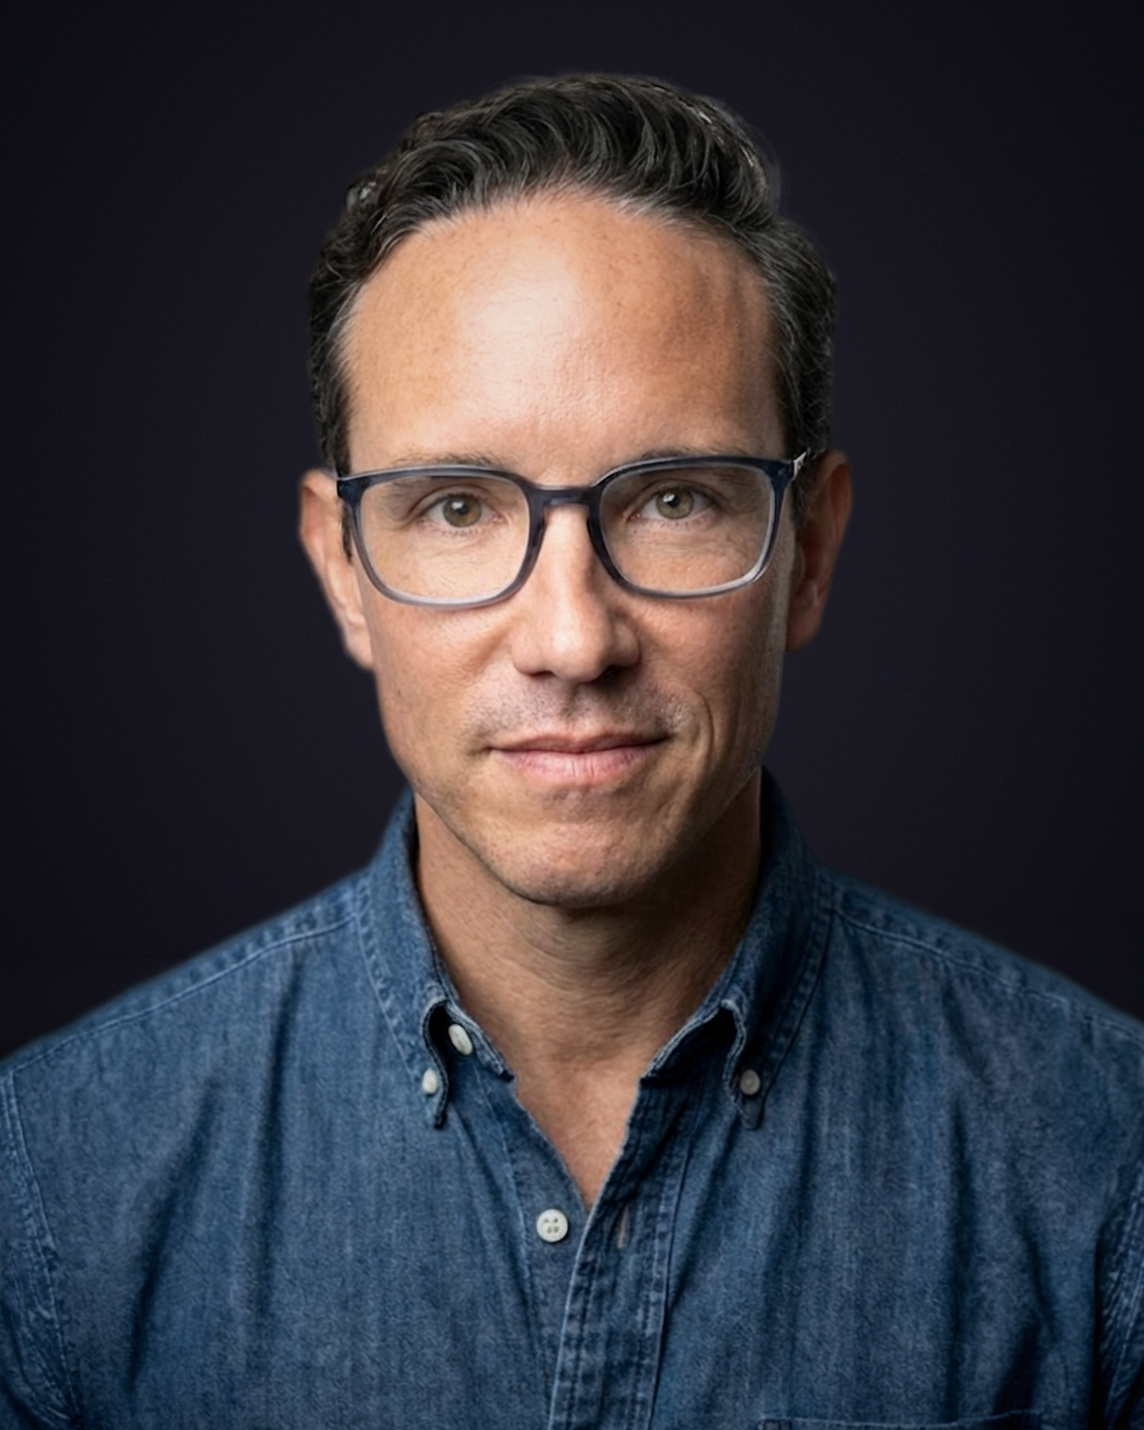
Gregory Scott Henson, Founder and CEO of BlackBunker

Gregory Scott Henson

Founder & CEO

I built BlackBunker because SMBs buy security tools nobody is watching.

I built Henson Group from a one-bedroom NYC apartment into one of Microsoft's largest global MSPs, then architected the merger that became ALIANDO, where I helped build the cybersecurity practice. Same problem at every size: companies buy eleven security tools and staff zero people to watch them.

I am a 20X founder, 4X CEO, and 50X angel investor known as The Startup King. I also founded Cloud Veterans, which has helped thousands of veterans move into tech.

I own the business side of BlackBunker: pricing you can read in ten seconds, contracts without surprises, and humans watching every alert.
Gregory Scott Henson signature
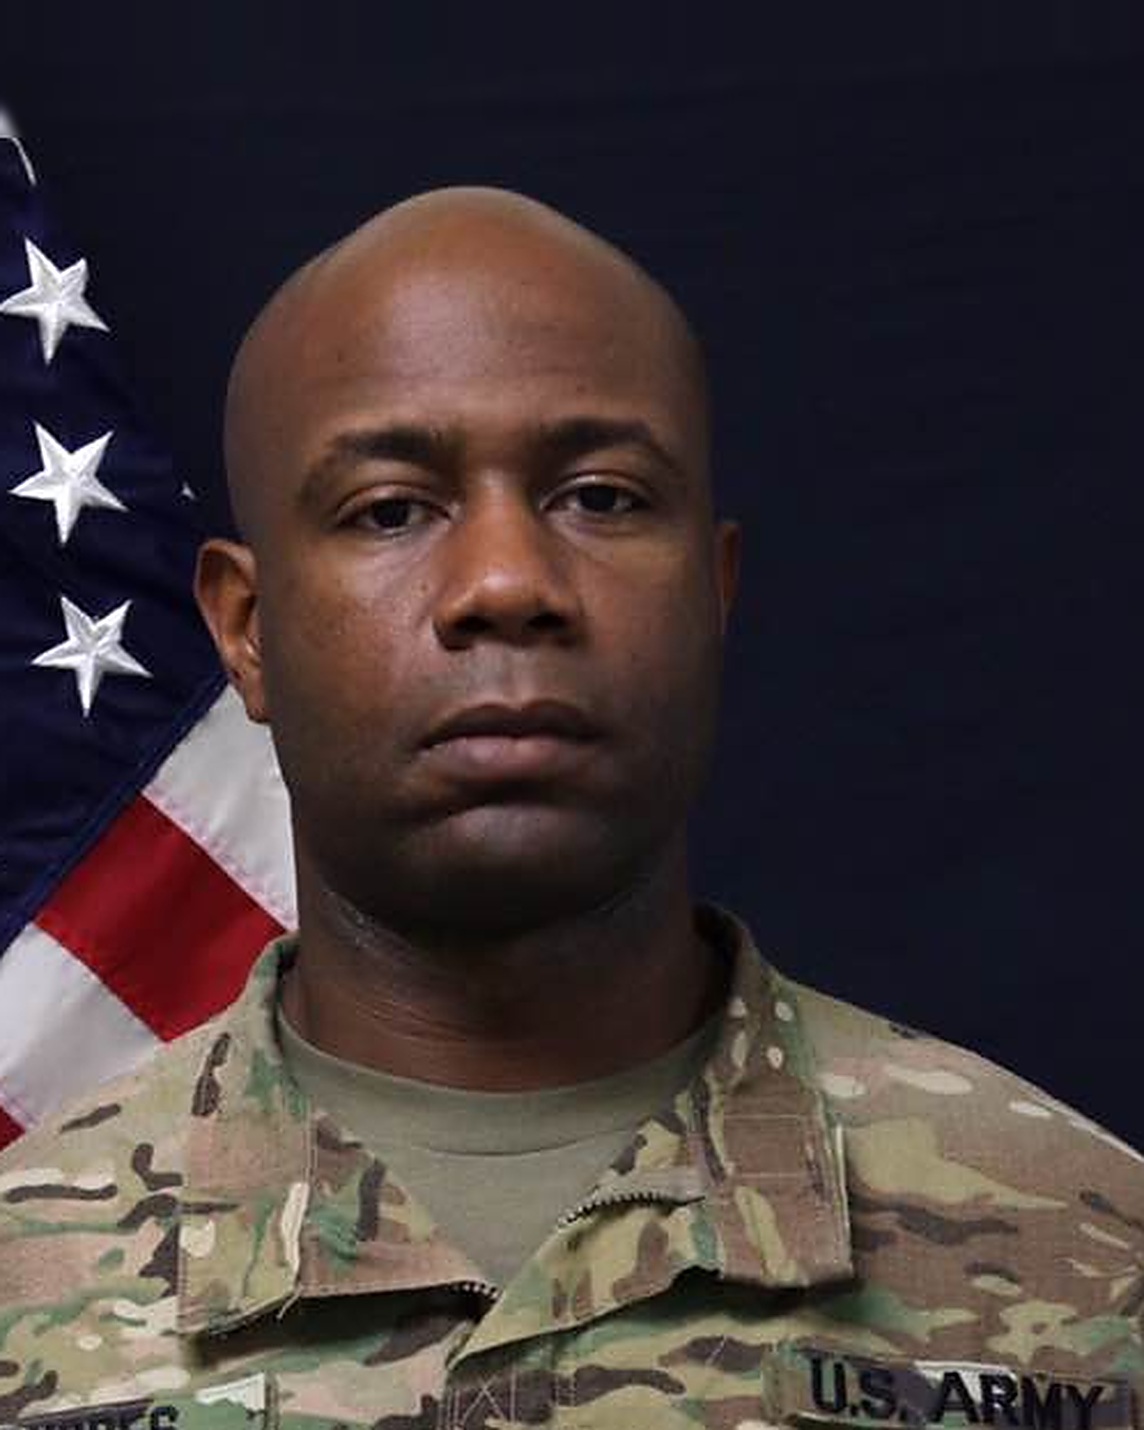
Kevin J. Rhodes Sr., Chief Technology Officer of BlackBunker

Kevin J. Rhodes Sr., MS, CISSP

Chief Technology Officer

I defended Army networks for 23 years. Your network gets the same watch.

Kevin spent 23 years as a U.S. Army cyber officer across Active Duty, the Army National Guard, and the Army Reserve, retiring in 2026. In the civilian world he has run information assurance programs as an Information System Security Manager at BAE Systems and at ARA, where he supported systems behind America's military nuclear planning. He managed vulnerability remediation and Risk Management Framework implementation for the U.S. Environmental Protection Agency, and before that ran hospital network infrastructure under HIPAA for Philips Health Systems.

He holds a CISSP and an MS, and has held clearance up to Top Secret.

Kevin owns the operations center: what we watch, how fast a human touches it, and what gets contained before you wake up.

Read the full story

// Questions

Frequently asked.

No. We stop attacks. Your compliance program is yours. Our incident logs and reporting will help it, but we are the people on shift, not the paperwork.

We contain first. Host isolation, session kill, token revocation, and infrastructure blocking are pre-authorized at onboarding. You are notified in parallel with a full timeline.

US citizens, US military veterans, working on US soil. Nothing is routed offshore or subcontracted. The Regulated tier adds contractual US-citizen-only staffing inside a government cloud enclave.

Your MSP keeps systems running. Nobody there is hunting threats at 2 a.m. We work alongside your MSP and hand them clean remediation tickets.

Month-to-month after onboarding. If we are not watching the way we said we would, you leave.

See all FAQs
Book a Call